Governance Establishes Accountability
Governance and risk management are sometimes viewed primarily as compliance activities. Policies are established, committees are formed, risks are documented, and controls are implemented to satisfy regulatory, audit, or organizational requirements.
These activities are important. However, governance and risk management should also help an organization operate more effectively and achieve its business objectives.
When properly integrated into the organization, governance establishes how decisions are made and responsibilities are assigned, while risk management helps management understand the conditions that could affect those decisions and objectives. Together, they can provide a foundation for improved business performance.
Effective governance begins with clearly defined responsibilities and decision-making authority.
As organizations grow, responsibilities frequently become distributed across business functions, management levels, and technology environments. Without clearly established accountability, important activities may be duplicated, inconsistently performed, or not performed at all.
Policies and governance structures can help define expectations, but documentation alone does not establish accountability. Individuals must understand what they are responsible for, what decisions they are authorized to make, when matters should be escalated, and how their responsibilities relate to those of other functions.
This clarity can improve more than compliance. It can reduce delays, improve coordination, and allow management to make decisions with a better understanding of who is responsible for carrying them out.
Connect Risk to Business Objectives
Risk management is most useful when risks are evaluated in relation to the objectives they could affect.
A risk register containing numerous technical, operational, financial, and compliance risks may provide useful information. However, its value is limited if management cannot determine which risks could have the greatest effect on organizational priorities.
For example, a technology risk may affect the organization's ability to process transactions, protect customer information, meet regulatory requirements, or maintain operations. An operational risk may affect revenue, service delivery, customer relationships, or the organization's ability to execute a strategic initiative.
Connecting risks to business objectives provides context for evaluating their significance.
It also helps management determine whether resources are being directed toward the risks that matter most.
Use Controls to Support the Business
Internal controls are also sometimes viewed primarily as restrictions placed on business activities. Effective controls, however, should support the organization while reducing risk to an acceptable level.
Poorly designed controls can create unnecessary approvals, duplicate activities, manual workarounds, and delays. In contrast, well-designed controls can improve the reliability of information, clarify responsibilities, reduce errors, and help processes operate more consistently.
The objective should not be to implement the greatest possible number of controls. It should be to establish controls that appropriately address risk while allowing the organization to operate effectively.
In some cases, improving the control environment may involve adding a control. In others, the better solution may be eliminating redundant activities, automating a manual process, clarifying ownership, or improving the information available to management.
Make Risk Information Useful for Decision-Making
Governance and risk processes often generate significant amounts of information. Risk registers, assessment results, audit findings, performance measures, and remediation plans can all provide valuable insight.
The challenge is converting that information into something management can use.
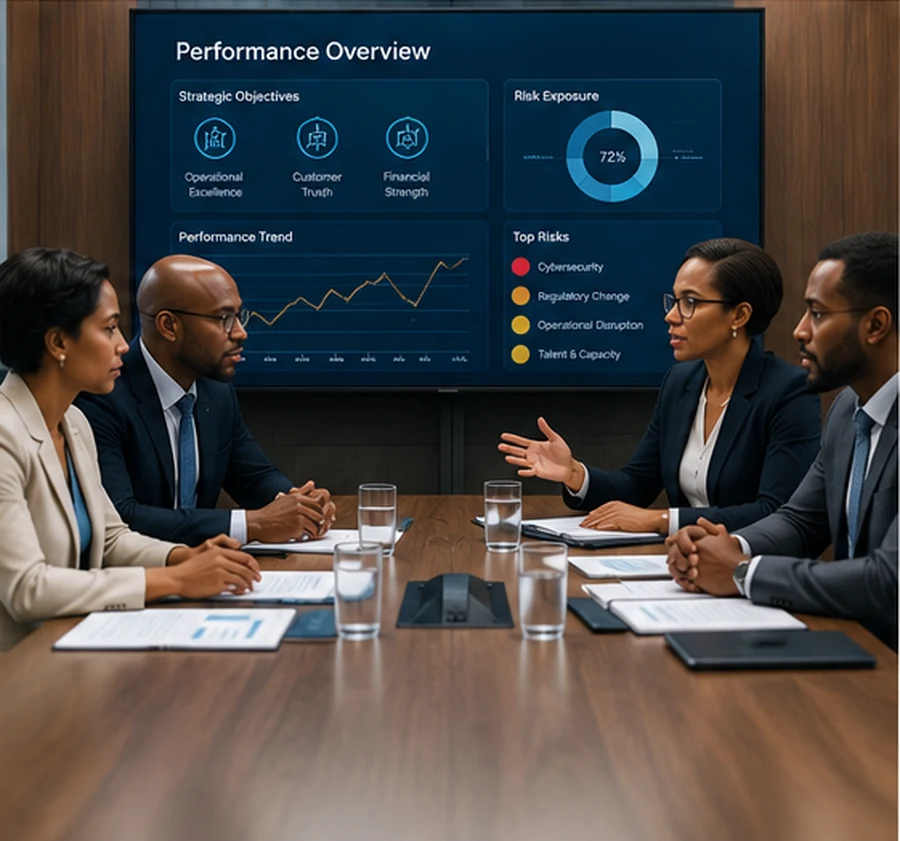
Reporting should help decision-makers understand which risks require attention, how those risks could affect organizational objectives, what actions are underway, and where additional decisions or resources may be necessary.
This requires more than reporting the number of open findings or assigning risks a rating. Management should be able to understand the broader implications of the information being presented.
When risk information is connected to business priorities, it becomes a management tool rather than simply a compliance record.
Governance and Performance Should Reinforce Each Other
Strong governance does not guarantee strong business performance, nor does risk management eliminate uncertainty. Both should, however, improve the organization's ability to make informed decisions and respond to changing conditions.
Organizations that clearly establish accountability, understand the risks to their objectives, implement practical controls, and use risk information to support decision-making are better positioned to direct resources where they can have the greatest impact.
Ultimately, governance and risk management should not operate alongside the business as separate compliance functions. They should be integrated into how the organization makes decisions, manages resources, and achieves its objectives.